


Malicious code substitutes links and redirects.
The provider blocked the site because of hidden scripts.
Malicious inserts in content and settings.
We'll check every PHP, JS, and HTML file.
We'll remove malicious inserts and hidden links.
We'll find and neutralize all hidden scripts.
We scan all files and the database. We find malicious code.
We remove shells, backdoors, and hidden scripts.
We test the site and make sure it's clean.
We provide a 30-day guarantee of cleanliness.
We scan PHP, JS, HTML, and other files.
We find malicious inserts in tables.
We neutralize all hidden scripts.
We remove rogue links from content and code.
Full cycle: diagnostics, cleanup, check.
We start work immediately after contact.
We remove malicious code as quickly as possible.
We have cured more than 350 Joomla sites. We work fast, provide a guarantee, and protect against re-infection.
We connect immediately after contact.
If the virus returns — we'll cure it for free.
We close vulnerabilities and configure a firewall.
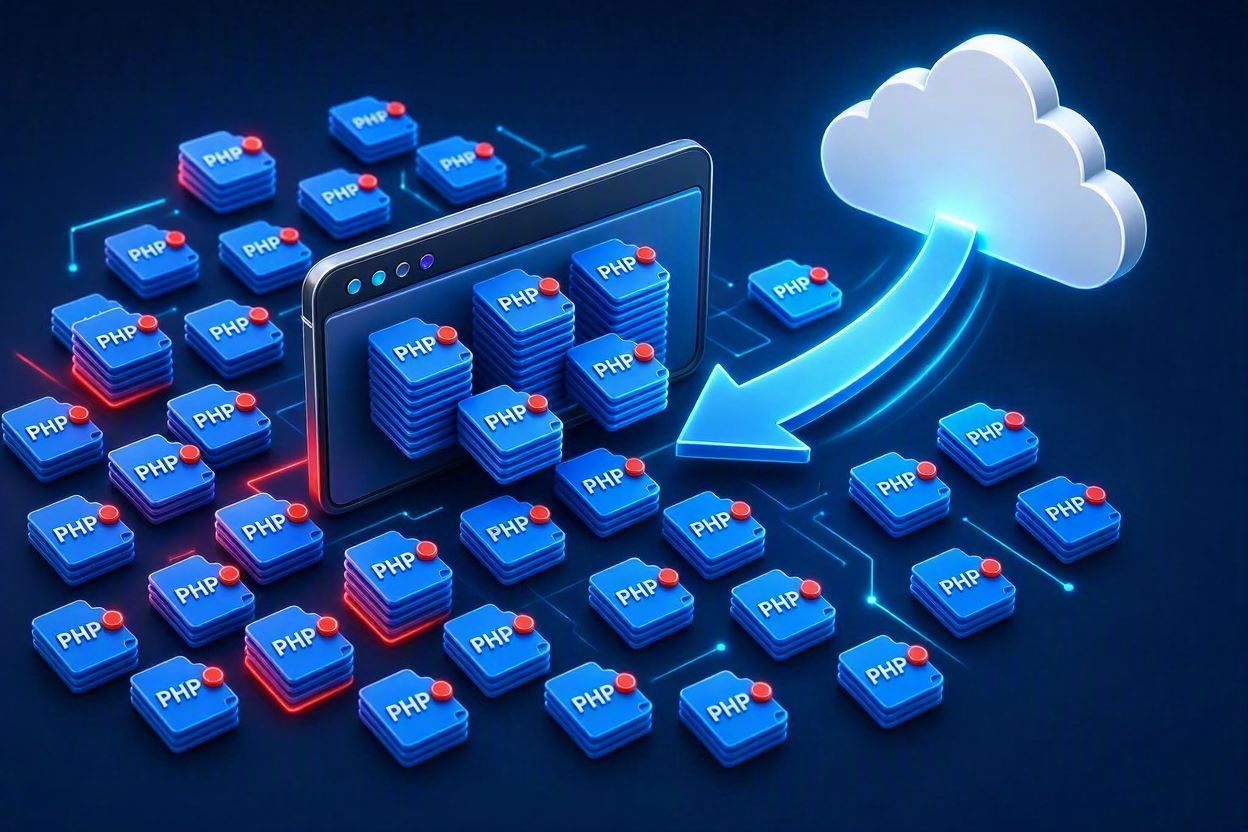
Массовое заражение файлов Joomla: как восстановить сайт без бэкапа Типичный сценарий: вирус проник на сайт и заразил все PHP-файлы — добавил вредоносную строку в начало каждого. Ручное удаление из со…

Что такое бэкдор и почему его нужно искать отдельно от вируса После взлома злоумышленник старается оставить себе запасной вход — бэкдор. Это может быть веб-шелл, скрытая учётная запись или модифициро…

Как проверить Joomla-сайт на скрытые вредоносные ссылки Злоумышленники внедряют на сайт ссылки на сторонние ресурсы: казино, аптеки, сомнительные магазины. Визуально ссылки не видны — они скрыты чере…
They found extraneous links in the site code. The team cleaned everything in one day and checked the database. Now the site is clean and runs faster.
The hosting blocked the site due to malicious code. In two days they cleaned everything and restored operation. Huge thanks!
They removed all shells and backdoors and closed vulnerabilities. Three months have passed — the site is clean, attacks have stopped.
Yes. Before starting we make a full backup. If something goes wrong — we roll back.
Regular cleanup — 1–2 days. Urgent — 2–4 hours.
Access to the site files and database. If you don't have access — we'll help you restore it.
Yes, 30 days. If malicious code appears again — we clean it free of charge.
We'll check for free and tell you what to do next. Response — 15 minutes.
